

📕Google Integration
Legacy guide to setting up Single Sign-On with Google Workspace.
This guide covers our previous SSO setup process. If you are setting up SSO for the first time, use the setup under Manage, then Single Sign-On in Spreo. It walks you through each step and shows the values to copy.
New setups use the single sign-on (ACS) URL https://spreo.io/login/saml2?p=YOUR-ACCOUNT-ID and the Entity ID https://spreo.io/YOUR-ACCOUNT-ID, not the values shown below.
Prerequisites
In order to configure Google SSO integration with Spreo you will need:
Admin access to your Spreo account.
Admin access to your organization's Google account.
One or more authorized domains adding to your Spreo account (see end of article).
A note of your organizations Spreo Account ID.
How to find your Spreo Account ID
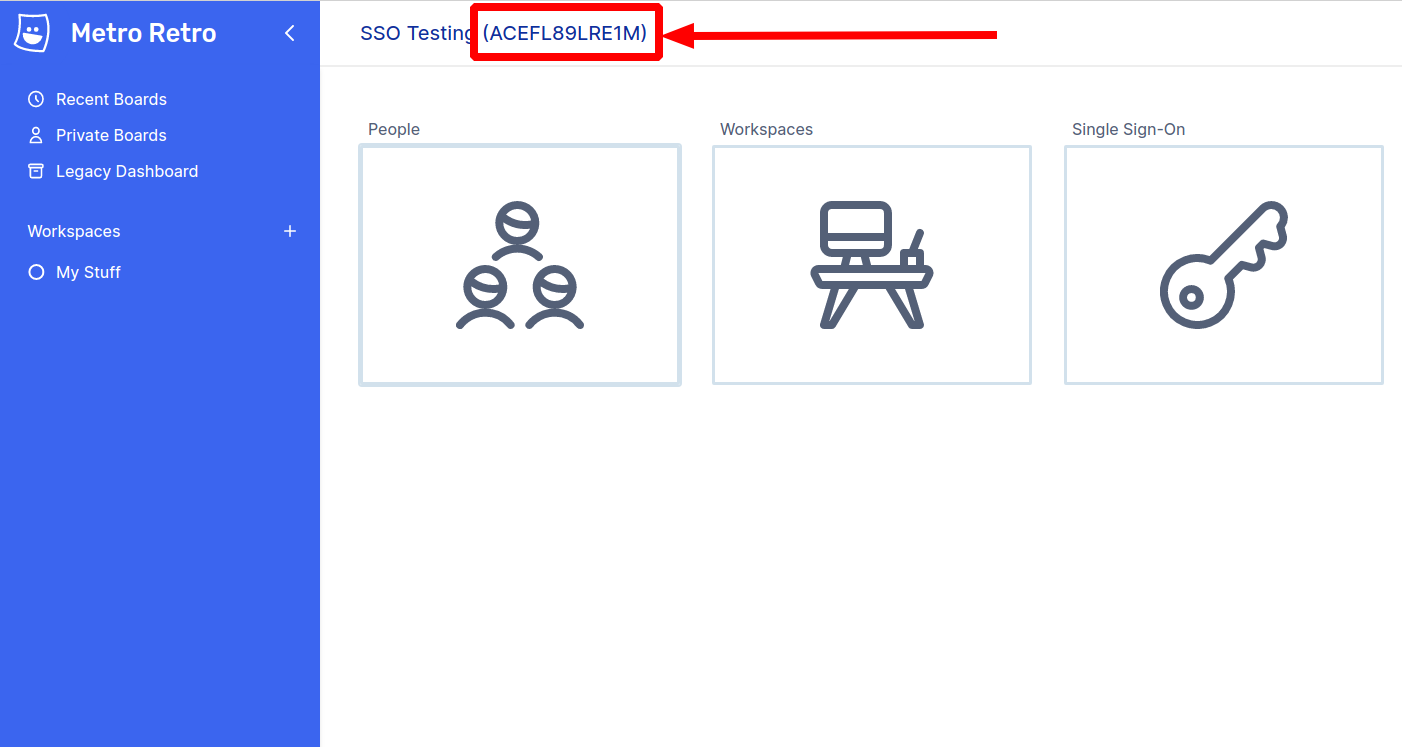
Before you begin, you will need your organization's 12 character Spreo Account ID. You can find this in the under the management menu within Spreo: https://spreo.io/manage
Integration Setup
From within the Google dashboard, choose Apps > Web and Mobile Apps from the left hand navigation. Then, click Add App and choose Custom SAML App.
Step 1 - App details
Set the name as Spreo and optionally add an icon. We recommend using this image as the icon: https://s.spreo.io/site/logo/logo-padded.png
Click Continue.
Step 2 - Google Identity Provider details
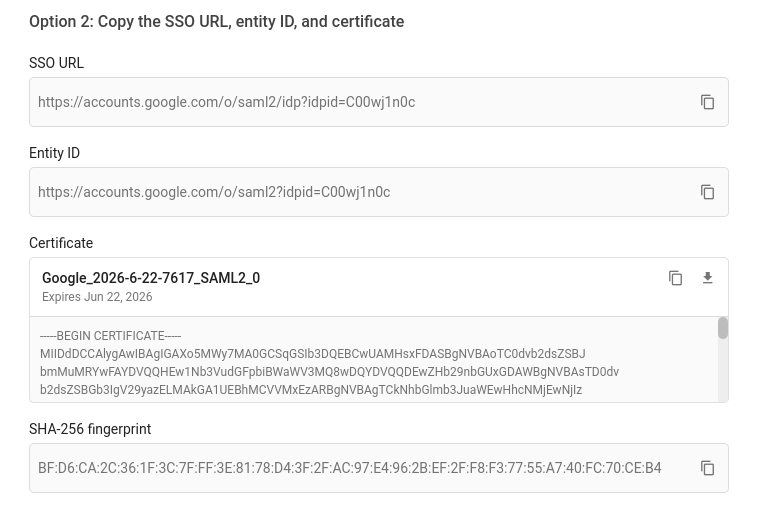
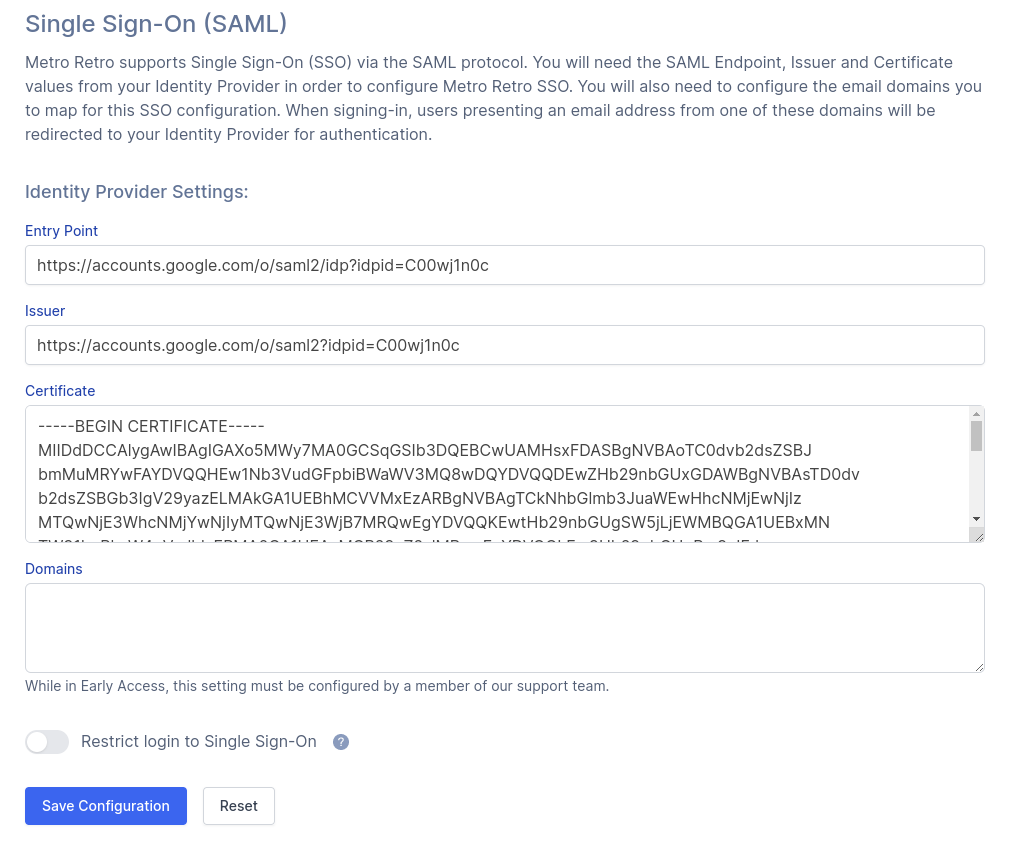
Here we will configure Spreo with the settings it needs to communicate with the Google IDP service. To do this, open a new tab/window in your browser and go to https://spreo.io/manage/security/sso.
Copy the settings from the Google screen into Spreo as follows:
For "Entry Point" use the "SSO URL" value
For "Issuer" use the "Entity ID" value
For "Certificate" use the "Certificate" value (note will be quite large).
Once copied, click Save.
Back on the Google page, click Continue.
Step 3 - Service provider details
On this screen we configure the Google side with the configuration it needs to communicate with Spreo.
Input the following settings:
For "ACS URL" use
https://spreo.io/login/samlFor "Entity ID" use your Spreo Account ID (see above on where to find this).
Leave all other settings as their defaults.
Click Continue.
Step 4 - Attribute mapping
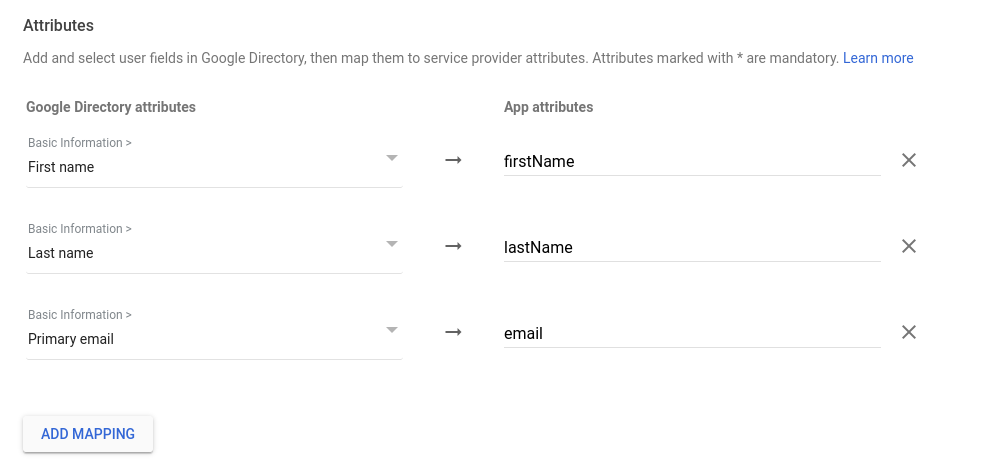
The final step is to configure which profile values Google will send to Spreo. We need to map three of these:
"First name" should be mapped to
firstName"Last name" should be mapped to
lastName"Email name" should be mapped to
email
Click Continue to complete the setup wizard.
Step 5 - Grant access
Depending on how your organization is configured, it's likely that Spreo will be OFF for all users by default. You can control which users have access to the app via the User Access screen available from inside the App information panel. The easiest way to configure this is to set the app ON for everyone.
Step 6 - Configure domains
If you have not already had your authorized domains configured by a Spreo team member, please contact us on Intercom or at contact@spreo.io to set these up. The domains must include all domains that your team will login from.
Last updated